
Why Native AI Wants Its Personal Checks
Native AI workflows rely closely on exterior mannequin platforms and code dependencies, creating distinctive safety challenges when working unverified open-source recordsdata domestically. To deal with these vulnerabilities, desktop mannequin administration platforms like Unsloth Studio mix repository integration with automated, multi-checkpoint scanning to safeguard runtime environments with out requiring guide setup.
One current case exhibits the danger: an infostealer hiding inside a Hugging Face repository. Hugging Face as a number one platform for downloading and sharing fashions was unknowingly internet hosting a repository with an infostealer. The repo impersonated OpenAI’s Privateness Filter launch and copied its mannequin card nearly verbatim. Its loader.py fetched and ran an infostealer on Home windows. Then the repository hit #1 trending and confirmed about 244,000 downloads, figures HiddenLayer says have been nearly actually inflated.
This episode exhibits why checks at load time are vital.
How Unsloth Formed Product Safety
Early on this desktop app has the reducing fringe of OSS and adapts shortly to altering environments. Unsloth established protocols to make sure optimum security to its finish customers. After in depth releases, for upcoming Open Supply AI week Unsloth printed a security overview for Unsloth Studio and Unsloth Desktop highlighting on a excessive stage how their safety works.
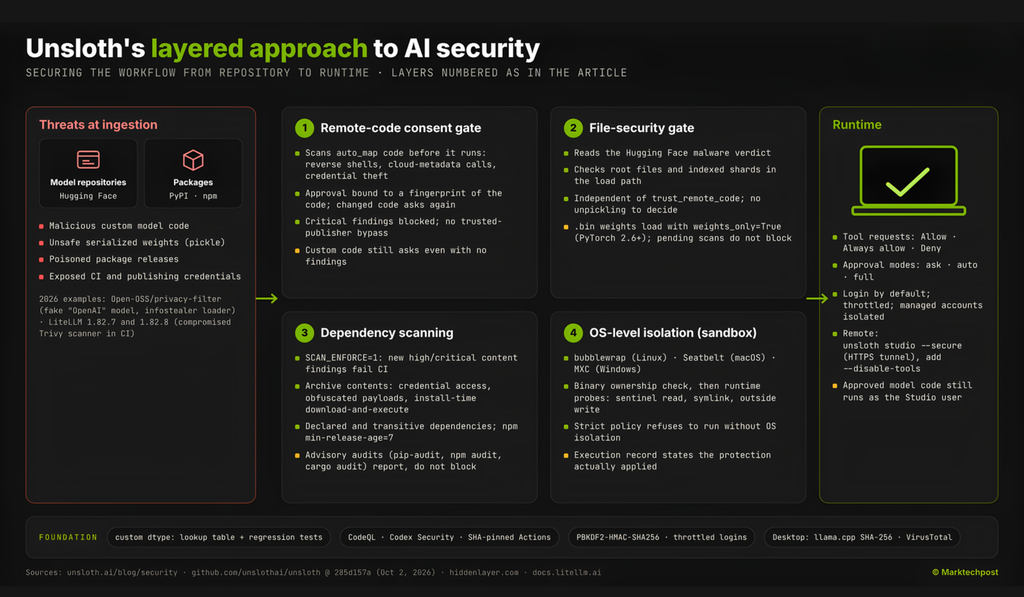
Whereas the desktop app maximizes for security in fine-tuning environments, customers nonetheless have a full vary of mannequin decisions. How Unsloth safety works is when a workflow strikes from downloading to executing it triggers a 4 checkpoint course of: fingerprint-bound code approval, a separate weight-file gate, probed OS sandboxes and enforced package-content scanning. These protocols have been established for cover by complimenting present controls quite than changing them, customers can hold advisory scans, pinned revisions, community limits and scoped credentials in place whereas leveraging checks. Taken aside every job serves a unique function in safety layering.
1. Approval follows the code, not the title
Think about approving a mannequin’s customized Python code, then returning after the repository modified. Ought to the previous approval nonetheless rely? Unsloth Studio says no. The repository exhibits it fingerprints the scanned code and re-checks that fingerprint, plus scanner model, on each load. A saved approval can silence a repeated dialog, and continues with a contemporary scan. Modified code requires contemporary consent. For adapter-plus-base hundreds, Studio evaluates each repositories, together with tokenizer, processor and nested configuration. Primarily if one thing has modified, Unsloth Studio will know.
Any change replace or change the previous fingerprint. Excessive- and medium-severity findings require approval matching the present fingerprint. If distant code should be inspected however can’t be retrieved, the load is blocked. A trusted writer will get no blanket exemption; a first-party repository can nonetheless be stopped. The scanner seems to be for concrete behaviors: opening a reverse shell, reaching cloud-metadata endpoints or stealing credentials. Studio invokes the gate from its inference, coaching and export employees. The scan is just not a sandbox. As soon as permitted, distant mannequin code runs unconfined because the Studio consumer. The supply notes static patterns could be evaded.
The gate already fires on popular models. deepseek-ai/deepseek-ocr asks for approval and exhibits an exec/eval discovering. moonshotai/Kimi-VL-A3B-Instruct additionally asks for approval, flagged for superior obfuscation. The approval dialog lists the findings earlier than you determine. Customized code nonetheless wants your permission even when the scanner finds nothing worrying. Unsloth eliminated eval calls and different problematic sections in its tailored unsloth/DeepSeek-OCR and unsloth/DeepSeek-OCR-2 repositories. Person can determine their mannequin and determine to approve or not approve inside the app.
2. When A weight-file warning turns into a loading determination
Unsafe serialized weights, together with malicious pickle recordsdata, create one other. Studio checks these recordsdata individually from remote-code consent. Customized Python is just one path to execution and Unsloth Studio was designed for a number of entry factors.
Since Hugging Face scans repositories for malware and exhibits warnings on the mannequin web page, studio reads these resultst and blocks flagged files within the path the chosen loader would deserialize. That features nested shards referenced by weight indexes. It reads the scan end result with out unpickling the flagged artifact. The gate is just not fail-closed. Per the repository, hundreds can proceed when scan metadata is unavailable or pending. Plain native mannequin folders aren’t coated. Unsloth’s PyTorch 2.6+ minimal means .bin weights load with weights_only=True and the conduct is testable. The take a look at repository mcpotato/42-eicar-street is blocked from loading as a result of the warning lists the unsafe recordsdata and confirms they have been by no means downloaded. Whereas lower than 1% of Hugging Face fashions have potential safety points so Unsloth creates processes for added safety highlights how strong the Unsloth Studio product is changing into as a testomony to open-source.
3. Look contained in the dependency
The March 2026 LiteLLM compromise exhibits advisory checks aren’t sufficient, as a result of a package deal can carry a well-recognized title and ship a malicious launch earlier than any advisory exists. Unsloth’s package-content scanners examine the archive itself on the lookout for credential entry, obfuscated payloads, executable startup recordsdata and install-time download-and-execute conduct. The Python scan covers declared and transitive dependencies. The npm scanner inspects downloaded tarballs with out working their set up lifecycle scripts. A modified payload reopens the discovering as a substitute of inheriting a everlasting exemption so the Unsloth advisory scans report however don’t block; content material findings are the enforced layer so Unsloth provides relevance guidelines on high of this.Solely allowlisted packages could run scripts and npm installs reject packages published fewer than 7 days ago. CI fails if an unreviewed package deal tries to run one. Installs use lockfiles and npm ci, and the installer upgrades customers to npm 11 or newer. Earlier than any npm ci or cargo fetch, lockfile_supply_chain_audit.py checks for indicators of Shai-Hulud-style injection. Linters examine for unsafe loaders and dynamic execution, with baselines to trace findings. Dependabot updates carry a 3-to-7-day cooldown. pip-audit, npm audit with signature checks, cargo audit, OSV-Scanner, Semgrep and TruffleHog run alongside the content material scans. The audit workflow’s personal feedback say it intentionally avoids Trivy, on account of an earlier 2026 compromise.
4. The sandbox should show itself
Sandbox verification has turn out to be very actual within the age of AI and modeling so an put in sandbox binary is a place to begin, not a assure. Unsloth Studio runs instruments inside OS-level sandboxes: bubblewrap on Linux, Seatbelt on macOS and MXC on Home windows. On Linux, it checks the bubblewrap binary and its guardian directories are system-owned and never group- or world-writable. Then, per the repository, it probes the boundary. Can sandboxed code learn a number sentinel file? Comply with a workspace symlink to it? Write outdoors the workspace? The probe additionally confirms that reputable workspace and child-process operations nonetheless work.
Customers nonetheless have choices and might choose an approval mode: ask, auto or full. In auto mode, community and filesystem imports are flagged for approval, and file paths want approval. Harmful shell instructions are blocked outright. Device requests present Enable, At all times enable and Deny buttons. A strict coverage refuses instrument execution when OS isolation is unavailable or a required workspace examine is incomplete. A permissive coverage could fall again to software program safeguards, and the execution document says so. Every record lists the backend, isolation standing, limitations and cleanup end result. HTML and MCP artifacts render in sandboxed frames with their very own Content material Safety Coverage.
The Linux sandbox permits community entry, has writable model-cache entry and shares the host kernel. Pair it with community restrictions and tightly scoped credentials, this course of serves as a closing gate examine.
Distant Entry and Desktop App
Having a number of customers on the app additionally permits for managed accounts: every consumer solely sees its personal folders, by no means the proprietor’s Hugging Face token. Managed accounts want the proprietor’s grant to make use of fashions and are blocked from working repository code. Just lately Unsloth introduced working with Jev and users managing their own decision model.
Unsloth’s security-audit workflow makes use of read-only repository permissions and non-persisted checkout credentials. Each GitHub Motion is pinned to a full commit hash, and outbound-network allowlists block surprising egress. CodeQL covers Python, JavaScript/TypeScript, Rust and GitHub Actions. Unsloth says it runs Codex Security and repeated Codex evaluations throughout improvement to catch safety points and bugs.
Library Entry and Modifications
Unsloth’s core library has focused hardening too by custom data-type handling utilizing a set lookup desk as a substitute of evaluating expressions. Inherited executable configuration fields are sanitized, and regression exams guard the repair. Studio’s middleware exams reject outsized chunked requests, catching situations a Content material-Size examine alone would miss with desktop releases get their very own checks.
Prebuilt llama.cpp binaries are verified towards SHA-256 digests, and Home windows signatures are audited individually. Each Unsloth Desktop launch is scanned with VirusTotal. 1 printed instance confirmed 0 detections throughout 70 distributors at scan time. Unsloth notes every end result applies solely to the recordsdata or commit checked at the moment.
What adjustments versus the easier strategy
| Options | The Unsloth Resolution |
|---|---|
| Belief a mannequin repository by title | Bind approval to a fingerprint of the code, together with mixed adapter and base targets |
| Deal with remote-code consent as the one model-loading examine | Add a separate gate for flagged serialized recordsdata within the chosen loading path |
| Detect a sandbox binary and assume isolation | Probe isolation on the host and document the efficient safety stage |
| Depend on vulnerability advisories alone | Implement package-content scans with finding-specific baselines and a 7-day npm launch age |
| Run native AI as 1 implicit trusted consumer | Password-protected, throttled, multi-user accounts with encrypted keys |

Past safety, Bettering the NPU expertise
Suggestions shared by Unsloth’s founders requires richer efficiency metrics on NPUs, together with tokens per second. The app additionally asks for the power to configure model-loading settings earlier than launch, as GPU fashions already enable. These are requested enhancements, not confirmed releases for higher visibility and management when working fashions domestically.
Reviewing Unsloth’s overview and a static supply assessment of the repository, our coated commit 285d157a. Launch availability is predicated on data supplied for this text. Approval modes, macOS and Home windows sandboxes, credential encryption, npm release-age guidelines and desktop checks come from the overview. Fingerprint-bound approval, sandbox probing, execution data and login thresholds come from the repository. A number of protections belong to Unsloth Studio and Desktop; dependency scanning and audit restrictions reside within the improvement workflow. They don’t routinely shield a pocket book that imports the standalone library.
Key Takeaways
- Unsloth Studio ties remote-code approval to a fingerprint of the scanned code; modified code wants contemporary consent.
- Hugging Face malware verdicts block flagged weight recordsdata within the loading path, unbiased of trust_remote_code.
- Instruments can run in OS sandboxes (bubblewrap, Seatbelt, MXC); on Linux the repository exhibits Studio probing isolation first.
- Package deal-content scans fail CI on new high- or critical-severity findings; npm rejects packages beneath 7 days previous.
- Studio is password-protected and multi-user by default, with throttled logins and encrypted API keys.
Sources
- https://unsloth.ai/blog/security
- https://github.com/unslothai/unsloth/tree/285d157a412fb30c11d223f85df84357d946a00a
- https://www.hiddenlayer.com/insight/malware-found-in-trending-hugging-face-repository-open-oss-privacy-filter
- https://www.theregister.com/2026/03/24/trivy_compromise_litellm/
- https://docs.litellm.ai/blog/security-townhall-updates
- https://jfrog.com/press-room/jfrog-report-warns-ai-governance-fails-as-software-supply-chain-attacks-hit-record-highs/
- https://huggingface.co/docs/hub/security-malware
Be aware:Because of the Unsloth workforce for the thought management / assets for this text. This text is supported by Unsloth.
The submit What Occurs When a Trusted Mannequin Repo Modifications? Unsloth Studio Re-Checks Earlier than It Runs appeared first on MarkTechPost.